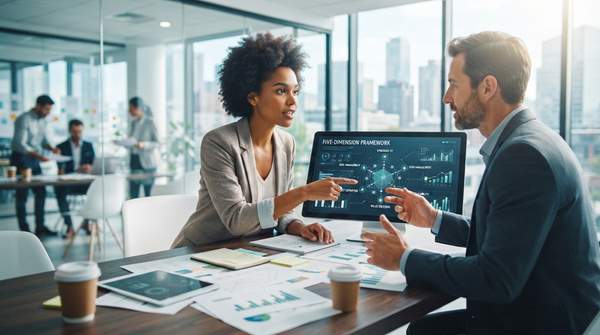
For most e-commerce startups expanding internationally, the most efficient path to cross-border payment compliance is not to build a compliance department in-house, but to work with a specialized payment provider while retaining strategic oversight internally. That is the consistent advice from payment industry sources: TransferMate argues that cross-border payments is "one area where working with a payment provider is almost certainly more efficient," while Nuvei recommends structuring compliance around a single high "global baseline" standard so that each new market only adds a small local "delta." This article explains those models and provides a decision framework to determine which approach fits your resources, target markets, and technology.
Introduction: Navigating Cross-Border Compliance for E-commerce Startups
Cross-border payment compliance spans several distinct regulatory domains: anti-money-laundering (AML) and know-your-customer (KYC) obligations, data residency rules, and consumer protection laws that vary by market. TransferMate describes this landscape as "multifaceted and constantly evolving," which makes it difficult for businesses to stay current on changes. For a startup, the core problem is that internal compliance checks "require expertise and time" — two resources a young company rarely has in surplus. The strategic question is therefore not how to master every jurisdiction, but how to structure your compliance operation so that the burden sits where it can be handled most efficiently.
One important caveat frames everything below: this is a strategic framework for decision-making, not legal advice. It does not detail the specific KYC, AML, or data residency laws of any particular country, and it is aimed at e-commerce startups and small to medium-sized businesses rather than large enterprises with established compliance departments.